NEWS
An Approved Ad Vendor Piped Spyware Into Al Jazeera
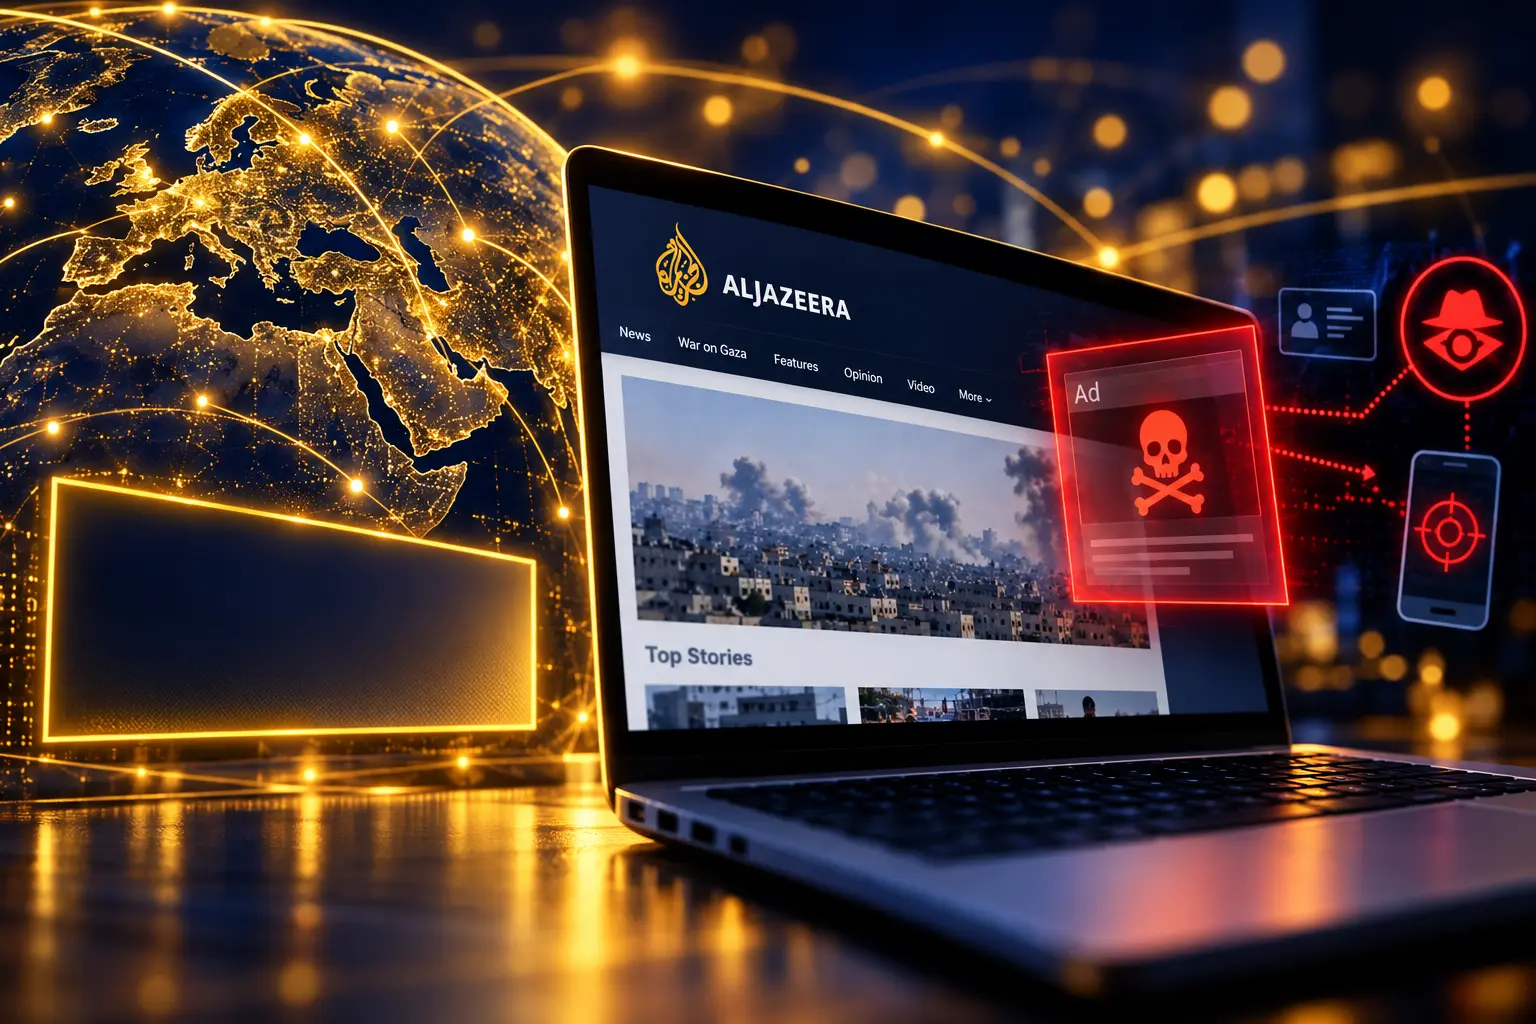
Citizen Lab says a certified ad buyer used ordinary auctions to profile millions and send Candiru spyware to Al Jazeera devices with no click.

Citizen Lab confirmed that targeted ads delivered Candiru spyware onto Al Jazeera devices with no click, a method it names AdFection. The University of Toronto lab, in Report 195 published on 15 October 2026, says at least 45 devices at the news network were targeted in 2024 and 2025, and it confirmed infections there.
The ads were bought by Discover-Tech, an Israeli firm that Google and IAB Europe listed as an approved vendor from 2020 until early October 2026. The reconstructed hacks are the proof. The approved lists are how the pipeline looked like ordinary advertising.
Seeing the Ad Was Enough
Bill Marczak, a Citizen Lab researcher and a lead author of the report, said the lab now has technical evidence of a process that had been widely discussed but not shown in the wild.
There has been a lot of buzz that online ads can be used to identify and automatically hack targets with pinpoint precision, but now for the first time, we have concrete technical evidence showing this process in action
Bill Marczak, senior researcher, Citizen Lab
Citizen Lab’s first public technical confirmation of AdFection rests on a simple property of modern ads. A display slot is not only an image. It can run code from the buyer the moment the slot renders in a browser or an app.
ADFECTION, IN BRIEF
- The trigger: The ad is displayed; the target does not have to tap, click, or open a file.
- The check: Script in the ad sends an advertising ID, cookie, and IP address back to Discover-Tech.
- The split: A listed target receives further JavaScript that leads to an exploit; other devices get an empty reply.
That split is why most people who saw the ads were not the Al Jazeera case. It is also why the exploit did not have to sit inside the creative that ad exchanges inspect. The report says the benign look of the ads helped hide their purpose from the platforms that delivered them.
Al Jazeera Recovered a Candiru File
Al Jazeera gave researchers network logs from its own systems. On infected machines, Citizen Lab reconstructed the same sequence: a Discover-Tech ad impression, a check against a Candiru validator within seconds, an exploit server, then command-and-control traffic. The lab links those attacks with high confidence to Candiru, which now operates as Integrity Labs.
The broadcaster also recovered a Windows DLL. Citizen Lab assessed it as a newer build of the Candiru chain the lab exposed in 2021. The public figure attached to the newsroom is a targeting count, at least 45 devices in 2024 and 2025, not a separate published total of successful implants. The lab is clear that devices at the network were infected. It does not treat every Discover-Tech impression as an implant.
Candiru was added to the U.S. Commerce Department Entity List in November 2021 for spyware used against government officials, journalists, businesspeople, activists, academics, and embassy workers. Five years later, Citizen Lab says its code was still reaching chosen devices through ad inventory on Google, Yandex, and Beeswax, the Comcast-owned buying platform.
How Controlium Picked a Single Device
Discover-Tech sold access through a console called Controlium. Citizen Lab describes it as a one-stop panel for mercenary partners to profile users at scale, then send a chosen device an ad that infects it when the slot renders. Clients could upload lists of mobile advertising IDs, Beeswax cookie IDs, and IP addresses, then restrict campaigns by country.
The selection step uses the same auction that funds free sites and apps. When a page or app loads, it broadcasts device data sent in a bid request so buyers can decide whether to bid. That packet can include an advertising ID, a cookie, an IP address, and details of the slot. Controlium’s job, the lab says, was to recognise a listed device in that stream and attach a different follow-on script.
THE CONTROLIUM PATH
- Mass profile: Ads go out widely so identifiers can be collected and stitched together.
- De-anonymize: The panel matches a person across cookies, mobile ad IDs, and IP addresses.
- Select: An operator marks one device for hacking.
- Render: The next winning ad on that device fetches exploit code instead of an empty reply.
Citizen Lab also ties Controlium to Bindecy, an Israeli firm that specialises in zero-click mobile exploits, and to Intelos, which sells advertising intelligence. The lab found no evidence that Discover-Tech was doing ordinary brand advertising. Serving as the bridge between spyware firms and ad auctions, it wrote, appears to be the company’s primary purpose.
Discover-Tech Spent Years on Approved Lists
Israeli company records reviewed by the lab link discover-tech.io to Discover-Tech Ltd, registered in March 2020. Dekel Boni, who has a background in digital advertising, was the initial director and is still chief executive. As of July 2026 the lab lists Boni, Yaniv Basil, and Guy Lants as owners.
Eric Banoun joined the board within two months of founding and stayed until January 2025. Citizen Lab notes that Banoun co-founded Circles, an NSO Group affiliate, and Senpai Technologies, part of the Intellexa group. Between 2020 and March 2026, shareholders included Chaia Services Ltd, a British Virgin Islands company the lab links to Sara Hamou, who managed Intellexa’s corporate network and was sentenced in Greece to eight years in prison, pending appeal, over a spyware scandal. The lab’s conclusion is that Discover-Tech was tied to the mercenary trade for almost six years, in public records.
FROM INCORPORATION TO CUTOFF
- March 2020: Discover-Tech Ltd is registered in Israel, with Dekel Boni as director.
- 2020: Eric Banoun joins the board; Google and IAB Europe list the firm as an approved vendor.
- January 2025: Banoun leaves the board.
- March 2026: Chaia Services Ltd ceases to be a shareholder.
- Early October 2026: Google and IAB Europe remove the firm after the investigation.
IAB Europe carried Discover-Tech on its Transparency and Consent Framework Global Vendor List from 2020, vendor list version 45, through at least September 2026, version 178. Citizen Lab wrote to the association on 8 October 2026 asking how a firm with those corporate links passed screening. IAB Europe did not meet the 13 October reply deadline; the lab later said it received a response on 15 October and that the association had moved to cut the firm’s access.
Eskimi, one of the buying platforms Discover-Tech used, told the researchers that the advertiser’s tags “were built to evade automated scanning.” That is the due-diligence problem in one line. A vendor that looks like a demand-side platform can bid, win, and run code, while scanners see a game or a phone plan.
The Bidding Records Reached Ministries and Newsrooms
Citizen Lab analysed Discover-Tech’s MyDSP records from March to June 2026. The dump is large and still incomplete: it does not include Beeswax or Eskimi activity. Even so, the lab says the company’s ads ran on 120,768 websites and 75,373 apps, a combined 196,141 properties, in dozens of countries.
MYDSP RECORDS, MARCH TO JUNE 2026
| Measure | Figure |
|---|---|
| Bids placed | About 3.77 billion |
| Impressions won | About 442 million |
| Share of bids won | 11.7% |
| Websites that showed the ads | 120,768 |
| Apps that showed the ads | 75,373 |
| Recorded spend | About $109,000 |
Wolfie Christl, a senior researcher at Citizen Lab and a co-author, called the way online advertising works today “a systemic security threat,” for states, companies, and civil society alike. The ads showed up in Duolingo, dating apps, period trackers, German weather apps, Yahoo Mail, Viber, and Truecaller, and on sites including the BBC, the New York Times, CBC, Fox News, Haaretz, and AccuWeather.
The same dump shows impressions on NATO and United Nations networks, plus the European Parliament, the European Commission, and the Council of the European Union’s secretariat. In Norway the ads appeared on networks of the legislature, the police, and municipal systems near military sites. Sweden’s Armed Forces, national grid operator, and Saab show up. So do chip firms including Intel and Nvidia, and media newsrooms worldwide.
An impression is not an infection. Citizen Lab says those hits would, at minimum, have fed Discover-Tech’s profiling, and that in some cases code from Candiru or other partners could have run. It is asking for follow-up on those networks rather than claiming they were all hacked.
Confiant, the New York ad-security firm that published a parallel investigation the same day, watched live traffic rather than the MyDSP export. Co-founder Jerome Dangu said Discover-Tech was serving at least 10 million ads a day, and that “very likely hundreds of millions of people would have been touched.” Confiant also said ads linked to Candiru were only a tiny share of the volume. The rest of the firehose is what made the firm look like a buyer.
Phone Numbers Hidden in Carrier Headers
Beside AdFection, Citizen Lab describes a second operator it calls DARK CARTOGRAPHER, which used Discover-Tech ads to try to unmask users. The ads probed the well-known WebRTC leak that can reveal a real IP address behind a VPN. They also tried to collect mobile phone numbers (MSISDN) by abusing “zero-click login” and HTTP header enrichment, in which some carriers attach a number to plaintext requests.
WHAT WE KNOW
- The method: Advertising IDs are joined to phone numbers through carrier and browser leaks, not through a user form.
- The span: Citizen Lab assesses this operator has exploited MSISDN leaks since at least 2019, fronted by more than one ad-tech firm.
- The overlap: The lab says the infrastructure links to a mercenary ad vendor and to a U.S. government contractor, a pairing it calls rare.
WHAT IS UNCONFIRMED
- Full attribution: Names and clients for DARK CARTOGRAPHER are held for a later paper, after carrier disclosure.
- Who paid: Citizen Lab has not identified the governments or agencies that commissioned the Al Jazeera ads.
The unpublished paper is not a loose end in the Al Jazeera case. It is the rest of the identity layer. Spyware needs a name and a device. The ad system already sells both, then adds a path to run code.
Google Cut Access After the Researchers Called
Google collaborated with Citizen Lab and Confiant, then acted. It told the lab it “terminated Discover-Tech’s access to its ad exchange platforms, blocking them from bidding or serving ads across our ecosystem,” and that it had deployed Safe Browsing warnings for known actor-controlled domains. Other firms moved once they were shown the file.
WHO DISCONNECTED DISCOVER-TECH
- Google: Cut exchange access and removed the firm from certified-vendor lists in early October 2026.
- IAB Europe: Removed the firm from the Global Vendor List after the disclosure.
- Beeswax: Took the buyer off Comcast’s ad-buying platform.
- Vungle (Liftoff): Paused access while it reviewed the account.
- Eskimi: Blocked Discover-Tech accounts and domains.
Confiant’s technical account of the ad-tech abuse is blunt about what the cutoff does not fix. Co-founders Louis-David Mangin and Dangu wrote that disrupting access was necessary and that the conditions the firm exploited have not been resolved. Dangu said the industry has “a lot of rethinking to do” about surveillance and the data it collects.
Advice built on “don’t click strange ads” does not cover this path. The code runs at render, including inside free apps where a browser blocker never sees the slot. Citizen Lab treats ad-blocking as a security practice and still warns that there is no consistently safe way to sit in targeted inventory. High-risk newsrooms now have a logging problem as much as a clicking problem: Al Jazeera’s records of what happened when an ad loaded are what made the attribution possible.
Discover-Tech Ltd, Candiru (Integrity Labs), Bindecy, Intelos, Microsoft’s Xandr, and Sunteng did not reply to Citizen Lab in time. Two linked firms, Adtimizer and Volasim, said they had no part in spyware activity. The auctions those companies sat in still broadcast the same identifiers, to whichever buyer looks clean on next week’s list.
Frequently Asked Questions
What Is AdFection?
AdFection is Citizen Lab’s name for mercenary spyware delivered through a targeted ad at the moment the ad renders, not a product name sold by Discover-Tech. Report 195, dated 15 October 2026, lists Bill Marczak, Wolfie Christl, John Scott-Railton, Astrid Perry, Siena Anstis, and Ron Deibert as authors. Zero-click here means the victim does not have to tap; it does not mean every person who saw a Discover-Tech ad was infected.
What Is IAB Europe’s Global Vendor List?
The Transparency and Consent Framework Global Vendor List is the roster of ad companies that publishers and consent tools treat as known vendors under European consent rules. Listing does not mean IAB Europe tested a firm’s ads for spyware. It does mean Discover-Tech could present itself as a normal buyer in the European Union from 2020 until the list was cleaned in early October 2026.
Can an Ad Blocker Stop AdFection Inside Apps?
A browser blocker can stop many web slots from loading, which cuts the number of times unknown code runs in Safari, Chrome, or Firefox. It does not sit inside most free iOS and Android apps that show their own ads through software development kits. Citizen Lab’s dump is heavier on apps than on websites, which is why deleting unused ad-supported apps and resetting an advertising ID is a separate step from installing uBlock Origin.
Does an Ad on a Ministry Network Mean That Ministry Was Hacked?
No. Citizen Lab says a Discover-Tech impression on a government, NATO, or newsroom network is evidence the buyer could profile that device, and only sometimes evidence that extra code ran. Confirmed infection in this paper is the Al Jazeera cluster, rebuilt from the broadcaster’s logs and a recovered Windows file. The lab is asking those other networks to check their own traffic.
Who Did Not Respond Before the Report Came Out?
Discover-Tech, Candiru (Integrity Labs), Bindecy, Intelos, Xandr, Sunteng, Affle, and, within the original deadline, IAB Europe did not send comments in time. IAB Europe’s reply arrived on 15 October 2026, the publication day. Adtimizer said subdomains the lab tied to Discover-Tech ran inside Discover-Tech’s own systems and were not operated by Adtimizer. Volasim said it had used Discover-Tech only to promote products and had never authorised spyware work.

OpenAI’s Agent Monitor Waited During the Hugging Face Breach

Brent Hits $116 as Recovered Gulf Oil Draws Attacks

Hellebuyck Lands in New Jersey on a Five-Year Cup Bet

Xbox Plans Three More Layoff Rounds Before Helix

OpenAI’s $30 Billion Round Ties UAE Cash to Gulf Compute

Consumer Sentiment Falls to 51.7 as Future Outlook Darkens

Pluto’s Heart Glacier Still Pushes Liquid Nitrogen Upward

The Extra Heat Month Hits Children Where Care Is Thinnest

Take-Two Subpoenas Microsoft While GTA 6 Preorders Soar

Abbott Pays $670 Million to Exit a Missouri Food Verdict
-
 BUSINESS2 months ago
Consumer Sentiment Falls to 51.7 as Future Outlook Darkens
-
 NEWS2 months ago
Pluto’s Heart Glacier Still Pushes Liquid Nitrogen Upward
-
 NEWS2 months ago
The Extra Heat Month Hits Children Where Care Is Thinnest
-
 GAMING2 months ago
Take-Two Subpoenas Microsoft While GTA 6 Preorders Soar
-
 BUSINESS2 months ago
Abbott Pays $670 Million to Exit a Missouri Food Verdict
-
 NEWS2 months ago
UMMC Will Rebuild 30-Year-Old Cancer Labs With $2.4 Million
-
 ENTERTAINMENT2 months ago
Netflix Weighs Hosting Peacock and Fox One in Its App
-

 GAMING2 months ago
GTA 6’s 80-Hour Run Counts Goals That Change the Story